Why Mathematics Must Protect the Freedoms Institutions Cannot Always Guarantee
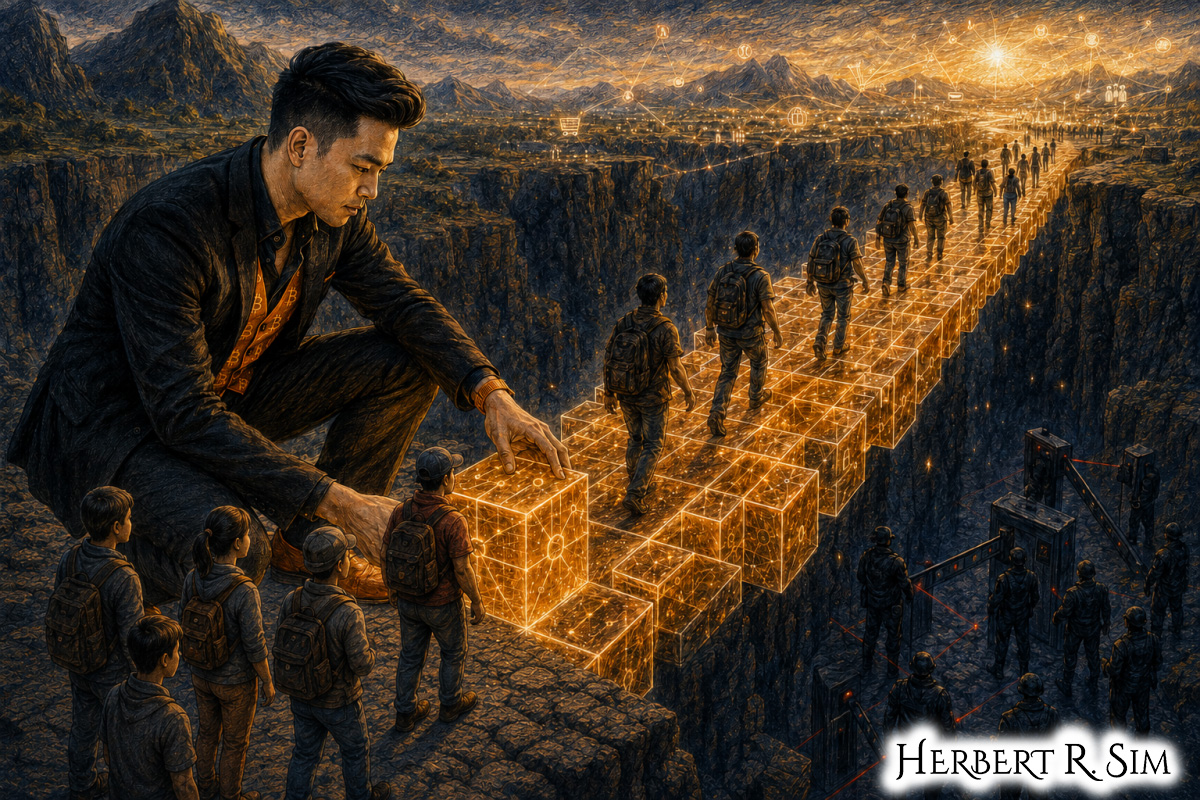
Above is my illustration entitled: “The Bridge Beyond Permission”. A vast chasm separates citizens from communication, commerce and information. I construct a glowing bridge from cryptographic blocks, allowing people to cross without checkpoints, gatekeepers or permission.
From Privacy to Protection
On March 9, 2013, I described privacy as sovereignty over disclosure.
Privacy gives the individual the authority to establish boundaries around his identity, communications, relationships and personal information.
But a boundary that exists only in principle remains vulnerable.
A privacy policy can change.
A confidential database can be breached.
A trusted employee can abuse access.
A company can be acquired.
A government can expand its surveillance powers.
A court can interpret an old law in a new way.
A service that promises confidentiality can still possess the technical ability to read everything entrusted to it.
Privacy therefore requires more than recognition.
It requires protection.
When I introduced Cypherpunkism on October 10, 2010, I identified cryptography as its principal technological defence.
In The Cypherpunkist Manifesto, I stated the principle directly:
Cryptography is applied freedom.
The Eight Principles of Cypherpunkism subsequently defined cryptography as freedom made technically enforceable.
And in Privacy Is Sovereignty, I described the relationship between the first two principles:
Privacy defines the boundary. Cryptography protects it.
This article develops the second principle more fully.
Cryptography is commonly presented as a technical subject involving algorithms, keys and computer security.
It is all of those things.
But it is also political.
Cryptography determines who can read.
Who can verify.
Who can authorize.
Who can possess.
And who must be trusted.
In a civilization increasingly governed through computer networks, these are questions about the distribution of power.
The Surveillance Question of 2013
During the past two weeks, public reports concerning United States government surveillance have revealed the scale at which modern communications may be observed and analyzed.
On June 6, The Guardian published a secret court order requiring Verizon Business Network Services to provide the United States National Security Agency with telephone metadata on an ongoing basis.
Subsequent reports described a classified surveillance program known as PRISM and raised further questions about government access to communications held by major technology companies.
The companies named in those reports disputed descriptions suggesting that the government possessed unrestricted or direct access to their systems.
The technical and legal details will continue to be debated.
But the larger lesson is already clear.
Digital communication creates records.
Those records accumulate inside systems operated by telecommunications providers, Internet companies and governments.
Once records exist, institutions can request, compel, copy, retain and analyze them at a scale impossible in the physical world.
In April 2013, before these disclosures became public, United Nations Special Rapporteur Frank La Rue warned that advances in communications technology had made state surveillance more effective and less visible. His report argued that communications surveillance must be governed by adequate law, legitimate purpose, necessity, proportionality and effective safeguards against abuse.
Law and oversight are essential.
But law alone cannot answer every technical question.
If a service provider holds every message in readable form, the provider remains capable of reading it.
If a central database contains a complete history of communication, that history remains available to whoever gains lawful or unlawful access.
If one authority possesses a universal means of decryption, that authority becomes a point of extraordinary power and an extraordinary target.
The present surveillance debate therefore leads directly to a Cypherpunkist question:
Must privacy depend entirely upon the restraint of institutions, or can individuals possess technological protection of their own?
Cryptography provides part of the answer.
From Institutional Promise to Mathematical Boundary
A law can declare that unauthorized parties should not read a communication.
A contract can promise that information will remain confidential.
A company can adopt a policy restricting employee access.
These protections matter.
But each depends upon institutional compliance.
Cryptography creates another form of protection.
Correctly implemented encryption transforms readable information—plaintext—into an unreadable form—ciphertext.
The information can then be recovered only by someone possessing the appropriate cryptographic key.
A policy says:
You should not read this.
Cryptography can establish:
You cannot read this without the key.
This distinction changes the balance of power.
The individual no longer depends exclusively upon an observer’s promise not to look.
The architecture itself can prevent unauthorized access.
Privacy without protection is a request. Cryptography can make it a rule of the system.
Cryptography does not make law unnecessary.
It does not eliminate the need for trustworthy institutions.
It does not transform every user into an independent island.
It gives the individual another layer of defence when trust fails, power changes or information passes through systems outside his control.
Freedom is stronger when it is defended by both institutions and architecture.
What Cryptography Makes Possible
Cryptography performs several distinct functions.
Each can protect a different dimension of individual sovereignty.
1. Confidentiality
Encryption can prevent unauthorized observers from reading information.
It can protect personal correspondence, financial records, medical information, business plans and stored files.
Confidentiality preserves the boundary between the intended participants and everyone else.
2. Integrity
Cryptographic hashes and signatures can help demonstrate that information has not been altered.
A document may remain visible while its integrity is cryptographically verifiable.
This protects individuals from records being silently changed and then presented as authentic.
3. Authentication
Cryptographic signatures can help verify that a message or action came from the holder of a particular key.
Authentication does not always require exposure of a complete legal identity.
It may establish continuity, authority or membership without revealing unrelated personal information.
4. Authorization
A cryptographic key can authorize access or action.
The holder of a key may unlock a file, approve a transaction, sign a document or control a digital asset.
This allows authority to arise from possession of the key rather than solely from permission granted by a central administrator.
5. Selective Disclosure
Cryptographic protocols may allow a person to prove a relevant fact without revealing every underlying detail.
A system may eventually allow someone to prove that he is authorized, qualified or above a required age without disclosing his complete identity.
This creates an alternative to the assumption that accountability requires total identification.
Cryptography can protect secrecy, verify truth, establish authority and reduce unnecessary disclosure.
Public-Key Cryptography Changed the Structure of Trust
Traditional encryption requires communicating parties to share a secret key.
This creates a practical problem.
How can two people establish a secure secret when they are communicating across an insecure network?
Whitfield Diffie and Martin Hellman’s 1976 paper, “New Directions in Cryptography,” introduced public-key cryptography and digital signatures as solutions to this problem.
Public-key systems use mathematically related keys with different functions.
A public key can be distributed openly.
A corresponding private key remains under the control of its holder.
Depending upon the system, others may use the public key to encrypt information intended for the holder or to verify a signature produced by the private key.
The political significance is profound.
Two individuals who have never met may establish secure communication without first receiving a shared secret from a central authority.
A person may publish a key that allows anyone to send him protected information.
A person may sign a message so that others can verify its origin and integrity.
Authority can be demonstrated mathematically rather than exclusively through an institutional registry.
Public-key cryptography allows trust to be reorganized.
It does not eliminate trust.
Users must still trust software, implementations, devices and methods of connecting keys to identities.
But it reduces the number of relationships in which complete institutional trust is unavoidable.
The Individual Must Control the Keys
Cryptography protects the individual only if authority over the keys is distributed appropriately.
A service may advertise encryption while retaining every decryption key itself.
Such a system may protect information from outsiders.
It does not necessarily protect the user from the service provider.
The provider may still read the information.
It may disclose the key.
It may be compelled to decrypt.
Its key database may be stolen.
Its administrators may abuse their authority.
A genuinely sovereign architecture should therefore ask:
Who possesses the private key?
Where practical, the individual should control the cryptographic keys governing his communications, identity and digital possessions.
This is not always simple.
Keys can be lost.
They can be stolen.
They can be copied without the owner realizing it.
They can become inaccessible when a device fails.
The stronger the individual’s authority, the greater his responsibility to protect it.
Sovereign systems must therefore develop practical methods for:
- secure key generation;
- safe storage;
- authentication;
- backup and recovery;
- revocation of compromised keys;
- and migration when technology becomes obsolete.
The objective is not merely to give users theoretical control.
It is to make individual control secure and usable in ordinary life.
Control of the key creates technological authority.
End-to-End Protection
Communication passes through many systems.
A message may travel from a personal device through a local network, an Internet provider, several intermediate systems and a service provider before reaching its recipient.
If the message remains readable at every stage, each stage becomes another point of exposure.
End-to-end encryption seeks to protect information from the sender to the intended recipient.
Intermediate systems may transport the message without possessing the keys required to read its contents.
This changes the role of the intermediary.
The intermediary remains useful.
But it no longer requires complete informational power over the communication it carries.
This principle can be compared with the physical postal system.
A postal service transports a sealed letter.
Its ability to deliver the letter does not require authority to read it.
Digital intermediaries should not automatically require more power than their physical predecessors.
A system should not require access to content merely because it provides transportation.
End-to-end encryption is not appropriate for every function.
Some services legitimately need access to information in order to process it.
But access should arise from genuine functional necessity—not from the assumption that intermediaries are entitled to observe everything passing through their systems.
Cryptography Should Be Available to Ordinary People
Governments use cryptography.
Militaries use cryptography.
Banks use cryptography.
Corporations use cryptography.
Their dependence upon encryption demonstrates that secure communication is not inherently suspicious.
It is essential infrastructure.
The individual should possess access to comparable principles of protection.
A private citizen’s correspondence may not carry national secrets, but it can contain medical information, financial details, family matters, professional plans and political opinions.
A small business may lack the resources of a multinational corporation, but its confidential information remains valuable.
A journalist may need to protect a source.
A lawyer may need to protect a client.
A doctor may need to protect a patient.
A political dissident may need to protect an entire network of vulnerable people.
Phil Zimmermann released Pretty Good Privacy in 1991 because he believed ordinary people needed access to strong cryptography for electronic mail.
PGP demonstrated that personal encryption could be distributed as software rather than retained exclusively within government and corporate institutions.
The principle remains important:
Privacy must not become a privilege available only to those powerful enough to purchase or command it.
Cryptographic protection should become easier to use, widely available and enabled wherever appropriate.
The ordinary person should not require the skills of a professional cryptographer merely to send a private message.
Code Is Speech—and Architecture
Cryptography is expressed through mathematics, research papers, algorithms and computer code.
To restrict the publication of cryptographic code is therefore not merely to regulate a machine.
It may restrict the communication of scientific knowledge and political ideas.
The legal dispute in Bernstein v. United States Department of Justice concerned Daniel J. Bernstein’s attempt to publish source code for an encryption system he had developed.
The case helped establish the principle that encryption source code can constitute protected expression.
This matters because code performs two functions.
It communicates an idea to people capable of reading it.
It also instructs a machine to implement that idea.
Cryptographic code is therefore both expression and architecture.
It explains how freedom can be protected and then performs the protection.
Eric Hughes summarized the practical ethos of the historical Cypherpunk movement:
“Cypherpunks write code.”
The Cypherpunk does not merely request private communication.
He builds it.
He does not merely criticize centralized authority.
He constructs alternatives.
He does not merely publish a philosophical argument.
He translates the argument into a functioning system.
Code is speech when it communicates an idea. Code is political architecture when it determines who possesses power.
Cryptography and Financial Sovereignty
Cryptography can protect more than communication.
It can authorize the transfer of value.
Satoshi Nakamoto’s Bitcoin system defines an electronic coin through a chain of digital signatures and uses a peer-to-peer network to establish a shared transaction history without relying upon one central monetary server.
Bitcoin remains a young and highly experimental technology.
It may encounter technical, economic and political problems that have not yet become apparent.
But it demonstrates a significant architectural possibility.
A private key can give its holder the authority to sign a transfer of digital value.
The network can verify that authorization without requiring the holder to surrender his private key.
Possession and authorization become cryptographically connected.
The individual does not merely possess an account granted by an institution. He may possess a key recognized by a network.
This does not abolish intermediaries.
Many people will continue to rely upon services for security, exchange, convenience and recovery.
But cryptography creates the possibility of direct technological authority where only institutional authority existed before.
Money is only one possible application.
The same principle may eventually influence digital identity, contracts, ownership, voting, certification and access control.
The Argument That Encryption Protects Criminals
Every serious defence of cryptography must address the strongest objection.
Encryption can be used by criminals.
It can conceal evidence.
It can frustrate legitimate investigations.
It can protect malicious communication.
These concerns are real.
But the same cryptographic systems also protect:
- financial transactions;
- government communications;
- medical information;
- commercial research;
- critical infrastructure;
- journalistic sources;
- political dissidents;
- and the private lives of ordinary citizens.
A deliberately weakened encryption system does not distinguish perfectly between legitimate authorities and hostile attackers.
A universal recovery mechanism creates a universal point of attack.
A hidden vulnerability intended for one institution may eventually be discovered by another government, a criminal organization, a commercial spy or an unknown intruder.
The central question is therefore not whether encryption can be abused.
Nearly every general-purpose technology can be abused.
The question is whether weakening protection for everyone produces more security or merely redistributes vulnerability.
The existence of encrypted criminal communication does not justify making every lawful user easier to observe and attack.
Society should investigate particular crimes through lawful, targeted and proportionate methods.
It should not treat universal insecurity as the necessary foundation of law enforcement.
Privacy and accountability must coexist.
So must cryptography and justice.
Cryptography Does Not Solve Everything
Cryptography is powerful.
It is not magical.
A strong algorithm can be defeated by a weak implementation.
An encrypted message can be exposed on an infected device before encryption or after decryption.
A secure protocol can be undermined by a stolen password.
A legitimate public key can be replaced by an attacker if users cannot authenticate it correctly.
Encrypted content may still produce unencrypted metadata concerning who communicated, when communication occurred and where participants were located.
A user can voluntarily disclose information after receiving it securely.
A private key can be lost forever.
An algorithm considered secure today may become vulnerable as mathematics and computing advance.
Cryptographic sovereignty therefore depends upon an entire system:
- sound algorithms;
- open and careful review;
- correct implementation;
- secure devices;
- authentic key distribution;
- responsible key management;
- clear user interfaces;
- and continuing adaptation as threats evolve.
This is another reason open knowledge matters.
Security should not depend upon hiding the design of an algorithm from public examination.
Widely studied systems allow cryptographers, researchers and developers to identify weaknesses before those weaknesses become invisible foundations beneath millions of users.
Strong cryptography requires strong implementation, strong devices and informed users.
My illustration “The Bridge Beyond Permission” work-in-progress. The art represents that cryptography enables individuals to act without centralized authorization.
Usability Is Part of Freedom
A cryptographic system may be mathematically secure and socially ineffective.
If ordinary users cannot understand it, they will avoid it.
If a single mistake destroys access permanently, they may surrender control to intermediaries.
If encryption requires complicated manual procedures for every message, private communication will remain unusual.
If warnings are confusing, users will ignore them.
If key verification is impractical, users may communicate securely with the wrong person.
Freedom that can be exercised only by experts is incomplete.
Cryptographic protection must become usable enough to disappear into ordinary life.
People should not need to understand the mathematics of an encryption algorithm before benefiting from it, just as they do not need to understand electrical engineering before using a light.
The complexity should be managed by well-designed tools without concealing important choices from the user.
Good cryptographic design should combine:
- strong protection;
- clear control;
- safe defaults;
- practical recovery;
- and honest communication about limitations.
Security and usability should not be treated as enemies.
A protection that people cannot use will not protect them.
Eight Tests of Cryptographic Sovereignty
A system claiming to protect users through cryptography should be examined through eight practical tests.
1. The Algorithm Test
Does the system use strong, publicly studied cryptographic methods rather than untested secrecy?
2. The Key-Control Test
Who generates, possesses and can reproduce the private keys?
3. The Intermediary Test
Can the service provider read protected content, or is protection maintained between the intended participants?
4. The Integrity Test
Can users detect whether information has been altered?
5. The Identity Test
Can users verify the relevant party without exposing more identity than the interaction requires?
6. The Recovery Test
Can a user recover from loss without giving another institution unrestricted authority over every key?
7. The Transparency Test
Can independent experts inspect the protocol, implementation or published specifications?
8. The Usability Test
Can ordinary people use the protection correctly without requiring specialist knowledge?
A system need not answer every test perfectly.
Different applications face different risks.
But these questions reveal whether cryptography genuinely transfers power toward the individual or merely creates the appearance of security.
The Responsibilities of the Keyholder
Cryptographic sovereignty creates responsibility.
The keyholder should:
- protect private keys from unauthorized access;
- use reputable and well-reviewed software;
- maintain secure backups where appropriate;
- revoke or replace compromised keys;
- verify important public keys before trusting them;
- keep devices protected from intrusion;
- understand what encryption does and does not conceal;
- respect the privacy of other participants;
- and avoid presenting experimental systems as infallible.
The possession of a key does not remove ethical obligations.
The ability to conceal an action does not make the action just.
The ability to authorize a transaction does not eliminate responsibility for its consequences.
Cypherpunkism defends technological freedom while recognizing moral agency.
Cryptography protects choice. The individual remains responsible for the choices he makes.
A Declaration of Cryptographic Freedom
I have the right to use strong cryptography.
I have the right to protect my communications from unauthorized observation.
I have the right to possess and control my private keys.
I have the right to verify the authenticity and integrity of information.
I have the right to communicate without granting every intermediary access to the contents.
I have the right to use a pseudonym where complete identification is unnecessary.
I have the right to study cryptography.
I have the right to write and distribute cryptographic software.
I have the right to build systems that minimize reliance upon centralized authority.
I have the right to protect digital possessions through keys under my control.
I have the right to question systems that claim to be secure while retaining unrestricted institutional access.
I have the right to demand that technological convenience does not require permanent informational surrender.
With these rights comes responsibility.
I must protect my keys.
I must use cryptography responsibly.
I must respect the privacy of others.
I must distinguish security from the illusion of security.
I must understand the limitations of the systems upon which I depend.
I must remain prepared to improve those systems when weaknesses are discovered.
Cryptography Is Applied Freedom
Political freedom has traditionally been defended through constitutions, laws, courts and institutions.
These remain essential.
The digital age introduces another defence:
Mathematics.
Mathematics does not care whether the observer is powerful.
It does not grant automatic access because an institution is wealthy.
It does not alter its rules because a government changes.
Correctly implemented cryptography applies the same mathematical boundary to every unauthorized observer.
This is its political significance.
Cryptography can transform confidentiality from a favour into a capability.
Authenticity from an assertion into a verifiable signature.
Possession from an entry in someone else’s database into control of a private key.
Trust from blind dependence into something that can sometimes be tested.
It does not create perfect freedom.
It does not prevent every abuse.
It does not make institutions unnecessary.
But it gives the individual practical power that no declaration alone can provide.
A right written in law tells an authority what it should respect.
A cryptographic system can limit what an unauthorized authority is technically able to do.
Privacy defines the boundary.
Cryptography protects the boundary.
Control of the key creates technological authority.
Code turns principle into architecture.
Cryptography is applied freedom.
References and Foundational Influences
- Shannon, Claude E. “Communication Theory of Secrecy Systems.” Bell System Technical Journal, Vol. 28, No. 4, 1949, pp. 656–715. DOI: 10.1002/j.1538-7305.1949.tb00928.x.
https://doi.org/10.1002/j.1538-7305.1949.tb00928.x - Diffie, Whitfield, and Martin E. Hellman. “New Directions in Cryptography.” IEEE Transactions on Information Theory, Vol. 22, No. 6, 1976, pp. 644–654. DOI: 10.1109/TIT.1976.1055638.
https://doi.org/10.1109/TIT.1976.1055638 - Rivest, Ronald L., Adi Shamir, and Leonard Adleman. “A Method for Obtaining Digital Signatures and Public-Key Cryptosystems.” Communications of the ACM, Vol. 21, No. 2, 1978, pp. 120–126. DOI: 10.1145/359340.359342.
https://doi.org/10.1145/359340.359342 - Chaum, David. “Security Without Identification: Transaction Systems to Make Big Brother Obsolete.” Communications of the ACM, Vol. 28, No. 10, 1985, pp. 1030–1044. DOI: 10.1145/4372.4373.
https://chaum.com/security-without-identification/ - May, Timothy C. The Crypto Anarchist Manifesto. Written in 1988 and circulated electronically to the Cypherpunks mailing list in 1992.
https://cryptochainuni.com/crypto-anarchist-manifesto/ - Zimmermann, Philip R. “Why I Wrote PGP.” Pretty Good Privacy, first publicly released in 1991.
https://www.philzimmermann.com/EN/essays/WhyIWrotePGP.html - Hughes, Eric. A Cypherpunk’s Manifesto. March 9, 1993.
https://cryptochainuni.com/cypherpunk-manifesto/ - May, Timothy C. The Cyphernomicon: Cypherpunks FAQ and More. Version 0.666, September 10, 1994.
https://cryptochainuni.com/wp-content/uploads/The-Cyphernomicon-Timothy-C-May.txt - Electronic Frontier Foundation. “Bernstein v. U.S. Department of Justice.” Litigation concerning the publication of encryption source code.
https://www.eff.org/cases/bernstein-v-us-dept-justice - Lessig, Lawrence. Code and Other Laws of Cyberspace. Basic Books, 1999.
https://cyber.harvard.edu/publications/1999/Code_And_Other_Laws_Of_Cyberspace - National Institute of Standards and Technology. Advanced Encryption Standard. Federal Information Processing Standards Publication 197, November 26, 2001.
https://www.nist.gov/publications/advanced-encryption-standard-aes - Callas, Jon, Lutz Donnerhacke, Hal Finney, David Shaw, and Rodney Thayer. “OpenPGP Message Format.” RFC 4880, Internet Engineering Task Force, November 2007.
https://www.rfc-editor.org/info/rfc4880/ - Nakamoto, Satoshi. “Bitcoin: A Peer-to-Peer Electronic Cash System.” 2008.
https://bitcoin.org/bitcoin.pdf - La Rue, Frank. “Report of the Special Rapporteur on the Promotion and Protection of the Right to Freedom of Opinion and Expression.” United Nations Human Rights Council, A/HRC/23/40, April 17, 2013.
https://ap.ohchr.org/documents/dpage_e.aspx?si=A/HRC/23/40 - Greenwald, Glenn. “NSA Collecting Phone Records of Millions of Verizon Customers Daily.” The Guardian, June 6, 2013.
https://www.theguardian.com/world/2013/jun/06/nsa-phone-records-verizon-court-order - Greenwald, Glenn, and Ewen MacAskill. “NSA PRISM Program Taps in to User Data of Apple, Google and Others.” The Guardian, June 7, 2013.
https://www.theguardian.com/world/2013/jun/06/us-tech-giants-nsa-data