Why Digital Systems Must Prevent Unnecessary Concentrations of Authority
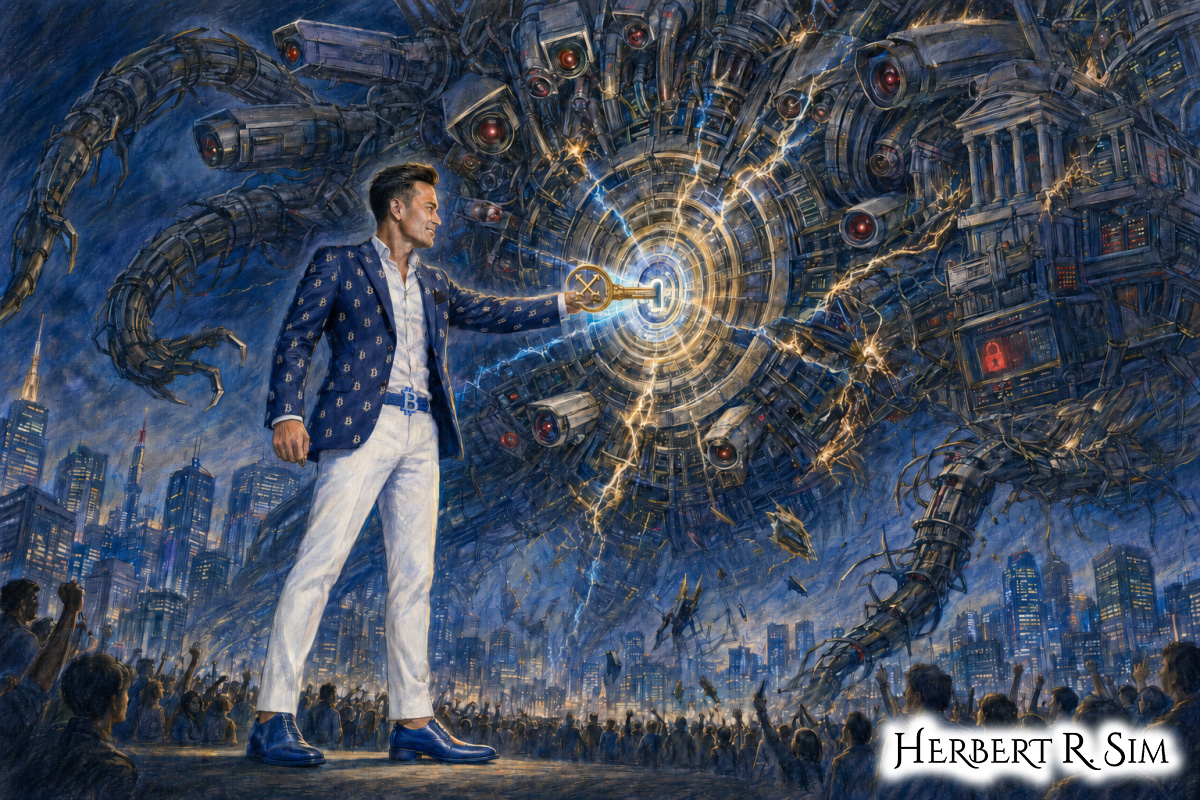
My illustration entitled “The Key Against the Leviathan” – A colossal mechanical leviathan formed from surveillance cameras, financial databases and censorship systems towers over a city. I insert a small but intensely luminous private key into its central mechanism, disabling its control network.
From Privacy and Cryptography to the Structure of Power
Cypherpunkism begins with the individual.
Privacy gives the individual authority over disclosure.
Cryptography gives the individual practical methods of protecting that authority.
But another question remains.
What happens when the entire system through which the individual communicates, publishes, identifies himself or exchanges value remains controlled by one institution?
A person may encrypt a message while depending upon a single platform to deliver it.
He may control a private key while depending upon one company to recognize his account.
He may own a copy of his information while one database remains the authoritative record.
He may possess the legal right to speak while one platform controls whether his audience can hear him.
He may possess digital money while one intermediary retains the ability to approve, delay or reverse every transaction.
Privacy and cryptography protect the individual within a system.
Decentralization examines the structure of the system itself.
When I introduced Cypherpunkism on October 10, 2010, I identified decentralization as its structural preference.
In The Cypherpunkist Manifesto, I described it as a technological check on concentrated power.
The Eight Principles of Cypherpunkism subsequently defined the principle:
Systems carrying extraordinary social power should, where practical, avoid unnecessary single points of control.
The first two dedicated principle essays—Privacy Is Sovereignty and Cryptography Is Applied Freedom—examined informational boundaries and their mathematical protection.
This article develops the third principle.
Decentralization is a check on power.
Every Centralized System Creates a Center of Authority
A centralized system has a center.
That center may be a government department.
A corporation.
A bank.
A server.
A database.
A platform administrator.
A certificate authority.
A payment processor.
Or a small group possessing privileged access to the rules.
Whoever controls the center may possess the ability to:
- determine who may participate;
- alter the authoritative record;
- observe activity across the system;
- approve or reject transactions;
- change the rules;
- remove information;
- disable accounts;
- identify participants;
- and exclude individuals without providing a viable alternative.
This authority may be exercised responsibly.
It may also be abused.
The central operator may be honest today and dishonest tomorrow.
It may be acquired by another organization.
It may become politically captured.
It may be compelled by a government.
It may suffer an internal failure.
It may be attacked from outside.
A system designed around a benevolent center remains designed around a center.
The character of today’s administrator is not a permanent safeguard against the powers granted to tomorrow’s administrator.
Cypherpunkism therefore examines authority structurally.
It asks not only whether those in control are trustworthy.
It asks whether anyone should possess that degree of control in the first place.
Centralization Is Not Automatically Oppressive
Centralization can be useful.
It can make decisions fast.
It can coordinate complex operations.
It can establish clear responsibility.
It can provide customer support.
It can reverse mistakes.
It can make systems easier for ordinary people to use.
A hospital requires organized authority.
A business requires management.
An emergency response requires coordination.
A court requires recognized procedures.
A software service may need administrators capable of repairing failures quickly.
Cypherpunkism should not become the simplistic belief that everything centralized is evil and everything decentralized is good.
A badly designed decentralized system may be slower, less secure and less accountable than a well-designed centralized one.
It may conceal responsibility.
It may waste resources.
It may be captured by technically sophisticated participants.
It may leave ordinary users without support or recovery.
The relevant question is not:
Is this system centralized?
The better question is:
How much power should any single point possess?
The more important a system becomes to communication, identity, money, knowledge or participation in society, the more carefully its concentration of authority should be examined.
Decentralization is not an aesthetic preference. It is a response to the consequences of concentrated control.
The Technological Form of Checks and Balances
Political systems have long recognized the dangers of concentrated authority.
Constitutions divide powers.
Courts review government action.
Legislatures debate executive decisions.
Federal systems distribute authority between national and regional institutions.
Competitive markets attempt to prevent a single company from controlling an entire industry.
The principle is not that authority must disappear.
It is that important authority should encounter limits, alternatives and counterweights.
Digital systems can embody a similar principle.
A network can route around a failed node.
A protocol can be implemented by competing providers.
A replicated record can be verified by multiple participants.
Open-source software can be examined and modified by independent developers.
A peer-to-peer system can allow direct interaction without requiring one operator to mediate every exchange.
A user can leave one application while remaining connected to the wider protocol.
Decentralization creates technological checks and balances.
It does not abolish power.
It disperses power among participants, implementations, nodes and institutions so that no single actor can easily control everyone else.
Distributed Is Not Always Decentralized
The terms distributed and decentralized are often treated as though they mean the same thing.
They do not necessarily.
A system may distribute its computers across many countries while remaining controlled by one company.
A corporation may operate thousands of servers while retaining one administrative authority capable of changing the rules for all of them.
A database may be replicated across many machines while one institution remains the sole owner of the authoritative record.
A service may use a peer-to-peer method for transferring information while requiring every user to receive permission from a central account system.
Distribution concerns where work, storage or communication occurs.
Decentralization concerns where authority resides.
A system can be technically distributed while remaining politically centralized.
The reverse may also occur.
A system may permit many independent authorities while relying upon infrastructure that is physically concentrated.
True decentralization must therefore be examined across several layers:
- Infrastructure: Who operates the servers, nodes and communication channels?
- Data: Who possesses the authoritative record?
- Identity: Who decides whether a participant is recognized?
- Protocol: Who determines the rules?
- Governance: Who can change those rules?
- Economics: Who controls the resources required to participate?
- Access: Who can exclude a user?
- Exit: Can participants leave without abandoning the entire network?
A system should not be called decentralized merely because it contains many computers.
The location of machines matters.
The distribution of authority matters more.
The Resilience of Distributed Networks
Paul Baran’s 1964 work on distributed communications compared centralized, decentralized and distributed network structures.
A centralized network depends heavily upon its central node.
Destroy or disable that node and the rest of the network may become unable to communicate.
A distributed network creates multiple possible paths.
If one node or connection fails, information may travel through another route.
This principle was originally examined in the context of communications survivability.
Its implications extend much further.
A system without one essential center may be more resistant to:
- technical failure;
- physical destruction;
- administrative error;
- political censorship;
- commercial collapse;
- and deliberate attack.
Redundancy may appear inefficient when every component functions perfectly.
Its value becomes visible when something fails.
A centralized system may be efficient in ordinary conditions and catastrophically fragile at its center.
Decentralization exchanges some simplicity for resilience.
Whether that exchange is justified depends upon the importance of the system and the consequences of failure.
Protocols Versus Platforms
A protocol establishes rules through which independent systems can communicate.
A platform provides a service controlled by a particular operator.
Both can be useful.
But they create different relationships of power.
Email is based upon protocols that can be implemented by many providers.
A person may change email providers while continuing to communicate with users elsewhere.
The provider is replaceable because the wider network does not belong exclusively to that provider.
A closed social platform operates differently.
A person’s contacts, identity, publications and reputation may exist entirely inside one company’s system.
Leaving the company may mean leaving the community.
The platform therefore acquires authority not merely because it provides a useful service, but because the cost of departure becomes increasingly high.
Open protocols reduce this dependency.
They allow different applications and providers to compete while remaining connected to the same broader network.
A provider can fail without destroying the protocol.
A user can leave one implementation without abandoning every relationship established through it.
Protocols preserve participation beyond the lifespan or permission of any single platform.
Decentralization Preserves Exit
Power increases when exit becomes impossible.
A user who dislikes one provider should be able to choose another.
A developer who disagrees with one implementation should be able to create a competing implementation.
A community that rejects a change should, where practical, retain the ability to preserve or adapt an earlier version.
Open-source software creates one form of exit through the ability to copy and modify code.
Open protocols create another through interoperability.
Portable data allows people to leave without abandoning their own information.
Distributed networks allow participants to communicate even when one operator refuses service.
The possibility of a fork can restrain those governing a project because participants are not necessarily trapped inside one implementation forever.
Exit does not eliminate conflict.
Competing versions can divide communities.
They can create confusion.
They can weaken network effects.
But the credible possibility of exit limits absolute authority.
A system is less sovereign over its users when its users can leave without losing everything.
Bitcoin as an Experiment in Decentralized Money
Money has traditionally required trusted institutions to issue currency, maintain accounts, process transactions and prevent the same funds from being spent twice.
Satoshi Nakamoto’s 2008 paper proposed another architecture.
Bitcoin uses digital signatures, proof-of-work and a peer-to-peer network to maintain a shared transaction history without placing the complete system beneath one monetary server.
Participants can verify the rules through open-source software.
Transactions are propagated through a network of nodes.
Miners compete to add blocks to the shared history.
No bank is required to maintain every Bitcoin balance.
No central administrator possesses a simple command capable of rewriting every participant’s copy of the ledger.
Bitcoin therefore demonstrates that a function traditionally assigned to a central intermediary can, under certain conditions, be distributed across a network.
But Bitcoin also demonstrates that decentralization is not absolute.
Mining power can become concentrated.
Users may depend upon centralized exchanges.
Software development may be influenced by a relatively small number of specialists.
Wallet providers may control users’ keys.
Internet infrastructure can create additional points of dependency.
A decentralized protocol can therefore develop centralized institutions around it.
Decentralization must be measured across the complete ecosystem—not inferred from the name of the protocol.
Bitcoin remains an experiment.
Its importance to Cypherpunkism lies not in declaring it perfect, but in demonstrating that monetary architecture can be reconsidered.
Ethereum and Programmable Decentralization
The launch of Ethereum’s Frontier network on July 30, 2015 extends the decentralized experiment beyond the transfer of digital currency.
Ethereum seeks to provide a distributed system through which programs and contractual instructions can be executed according to shared network rules.
The idea is significant.
If a network can agree upon more than account balances, decentralized architecture may eventually support:
- conditional transactions;
- digital agreements;
- registries;
- shared applications;
- and new forms of organization.
Ethereum is extremely young.
Its security, governance, scalability and practical uses remain uncertain.
Code can contain errors.
A decentralized program can execute a bad instruction as faithfully as a good one.
Removing a central administrator also removes the authority that might otherwise reverse a mistake.
This is why decentralization must be accompanied by careful engineering and clear responsibility.
Removing the intermediary does not remove the consequences of bad design.
Ethereum should therefore be understood as another experiment in the distribution of technological authority—not proof that every institution can or should be replaced by code.
Decentralized Publication and Knowledge
Publication becomes vulnerable when every document depends upon one server, domain, company or government-controlled gateway.
A central operator can remove material.
A hosting company can terminate service.
A domain can be seized.
A platform can alter visibility.
A server can fail.
Peer-to-peer file distribution demonstrates another model.
BitTorrent distributes pieces of a file among participants rather than requiring every download to come from one central source.
The more participants possess and share the file, the less the system depends upon its original publisher.
The InterPlanetary File System, proposed by Juan Benet in 2014, explores a content-addressed, versioned and peer-to-peer method of storing and distributing information.
Instead of locating information only by asking which server hosts it, content-addressed systems can identify information through a cryptographic representation of the content itself.
IPFS remains experimental.
But it illustrates an important principle:
Knowledge can be addressed by what it is rather than depending entirely upon where one authority permits it to remain.
Decentralized publication can make censorship and destruction more difficult.
It also creates challenges involving unlawful material, accuracy, persistence and responsibility.
Resilience must not become an excuse to ignore harm.
The goal is not to create a world without accountability.
It is to prevent one gatekeeper from possessing unilateral control over the circulation of lawful knowledge.
Decentralization and Private Communication
Cryptography protects the contents of communication.
Decentralization can protect the route and availability of communication.
If every message must pass through one provider, that provider possesses significant authority over access and metadata.
It may determine who can communicate.
It may retain records of relationships.
It may be compelled to block particular users.
It may fail and silence everyone simultaneously.
Peer-to-peer and distributed communication systems can reduce reliance upon one intermediary.
Tor provides one example of distributed routing designed to reduce the ability of any single relay to connect a user’s identity with his destination.
Tor does not eliminate every form of observation.
Its security depends upon software, network conditions, relay diversity and user behaviour.
But it demonstrates how authority over communication can be divided so that no single intermediary necessarily sees the complete relationship.
Privacy becomes stronger when no unnecessary participant possesses the complete picture.
Decentralized Identity
Digital identity is commonly granted through centralized accounts.
A platform creates an identity.
The platform stores its credentials.
The platform determines whether the identity remains valid.
The platform can suspend or erase it.
This arrangement may be convenient.
It also makes identity conditional upon institutional permission.
Cryptographic keys create the possibility of identities that are not entirely granted by one provider.
A person may control a key and use it to establish continuity across different systems.
Different institutions may provide claims or credentials without one institution owning the complete identity.
Such systems remain difficult.
People lose keys.
Names and reputations require social recognition.
False identities can facilitate fraud.
Recovery can reintroduce central authority.
But the objective is important:
The individual’s ability to exist digitally should not depend entirely upon one institution’s willingness to recognize him.
Decentralization Does Not Eliminate Power
Power does not disappear when a central administrator is removed.
It changes form.
Technical experts may acquire influence because few people understand the system.
Participants with more computing power, money, bandwidth or reputation may dominate decisions.
Large intermediaries may emerge around an open protocol.
Early participants may acquire advantages unavailable to later users.
Informal leaders may exercise authority without formal accountability.
A nominally decentralized system may gradually develop new centers of power.
This does not invalidate decentralization.
It means decentralization must be examined continuously.
The relevant questions include:
- Can new participants enter?
- Can independent implementations compete?
- Can users verify the rules?
- Can one participant censor everyone else?
- Can concentrated resources capture the system?
- Can the community remove a harmful dependency?
- Can users leave or fork?
- Can authority be challenged?
A decentralized system can still produce centralized outcomes.
The philosophy must therefore judge the actual distribution of power rather than accept the system’s description of itself.
The Problem of Accountability
Centralized institutions make responsibility easier to identify.
A company has directors.
A bank has officers.
A government department has legal authority.
A platform has administrators.
When a decentralized system fails, responsibility may be unclear.
Was the protocol defective?
Was the software implemented incorrectly?
Did users accept an unreasonable risk?
Did powerful participants manipulate the system?
Who should repair the harm?
Who possesses the authority to intervene?
Decentralization can prevent abuse by an administrator.
It can also make necessary intervention difficult.
This is especially important when systems govern money, identity or irreversible transactions.
A serious philosophy of decentralization must therefore address:
- dispute resolution;
- fraud;
- software defects;
- recovery;
- governance;
- and responsibility for foreseeable harm.
Freedom from centralized authority does not mean freedom from responsibility.
Decentralized governance must make accountability visible without quietly reconstructing the absolute authority it was designed to avoid.
My illustration “The Key Against the Leviathan” work-in-progress – represents that properly applied cryptography allows individuals to resist institutions vastly more powerful than themselves.
When Should a System Be Decentralized?
Not every system requires decentralization.
The costs may exceed the benefits.
A system presents a stronger case for decentralization when:
- one operator could censor lawful participation;
- failure of one institution would disable everyone;
- the authoritative record carries extraordinary social or economic importance;
- participants do not share a trusted intermediary;
- institutional power is difficult to challenge;
- the system crosses political borders;
- users require continuity beyond the lifespan of one company;
- and open participation creates meaningful public value.
A system presents a stronger case for central coordination when:
- rapid intervention is essential;
- clear legal responsibility is required;
- participants have deliberately chosen a trusted administrator;
- mistakes must be reversible;
- the costs of distributed consensus would be excessive;
- or the system performs a limited function without creating substantial dependency.
Many successful systems will combine both approaches.
They may centralize functions requiring coordination while decentralizing functions carrying dangerous concentrations of authority.
They may use independent providers operating through a shared protocol.
They may distribute verification while retaining identifiable institutions for support and accountability.
The objective is not maximum decentralization. It is appropriate decentralization wherever concentrated power creates unacceptable risk.
Eight Tests of Decentralized Power
A system claiming to be decentralized should be examined through eight practical tests.
1. The Control Test
Can one organization change the rules for everyone else?
2. The Failure Test
Can one technical or institutional failure disable the entire system?
3. The Censorship Test
Can one actor prevent lawful participants from communicating, publishing or transacting?
4. The Verification Test
Can independent participants verify important records and rules?
5. The Entry Test
Can new providers, developers or nodes participate without receiving permission from an incumbent gatekeeper?
6. The Exit Test
Can users leave one provider or implementation without abandoning their information, identity and relationships?
7. The Concentration Test
Have economic resources, infrastructure or governance gradually concentrated in a small group despite the distributed design?
8. The Accountability Test
Can participants identify responsibility and seek remedies when harm occurs?
A decentralized system need not answer every test perfectly.
Decentralization exists in degrees.
These questions reveal whether the architecture genuinely limits concentrated authority or merely hides it behind technical complexity.
The Responsibilities of the Participant
Decentralized systems transfer responsibilities toward participants.
A participant should:
- understand the essential rules of the system;
- protect the keys and credentials under his control;
- verify rather than trust blindly where verification is practical;
- support diverse implementations and infrastructure;
- avoid contributing unnecessarily to new points of concentration;
- recognize the limits of irreversible systems;
- communicate risks honestly;
- participate in governance where participation is available;
- and respect the sovereignty of other users.
A decentralized network cannot remain resilient if everyone depends upon the same gateway.
An open protocol cannot remain open if users refuse to understand or defend it.
A peer-to-peer system cannot function if every participant wants the benefits while contributing nothing to the network.
Decentralization is sustained by participation, not merely declared by software.
A Declaration Against Unnecessary Centralized Power
I do not reject institutions.
I reject unnecessary dependence upon institutions that cannot be challenged, replaced or left.
I do not reject coordination.
I reject the assumption that coordination requires absolute control.
I do not believe every system must be decentralized.
I believe every concentration of important digital power must be justified.
I have the right to build alternatives to centralized systems.
I have the right to participate in open networks.
I have the right to verify rules that govern my digital possessions and identity.
I have the right to communicate without requiring permission from an unnecessary intermediary.
I have the right to choose between competing providers.
I have the right to retrieve my information and leave.
I have the right to support a competing implementation.
I have the right to question those who control the center.
I have the right to seek decentralized alternatives when concentrated authority threatens freedom.
With these rights comes responsibility.
I must evaluate decentralization critically rather than romantically.
I must recognize hidden concentrations of power.
I must accept responsibility for the authority placed in my hands.
I must contribute to the resilience of systems from which I benefit.
I must distinguish freedom from the absence of accountability.
I must remember that decentralization is a means.
Human sovereignty is the purpose.
Decentralization Is a Check on Power
The political question of the digital age is not merely who governs a territory.
It is who controls the network.
Who controls the database.
Who determines identity.
Who approves the transaction.
Who can remove a publication.
Who can change the rules.
Who can exclude a participant.
And whether anyone can leave.
Centralized systems may answer every question with the same institution.
Decentralized systems attempt to divide those powers.
They allow communication to survive the failure of one node.
They allow verification beyond one database.
They allow participation beyond one provider.
They allow users to possess keys rather than merely accounts.
They allow protocols to survive the companies implementing them.
They preserve the possibility of exit.
Decentralization does not guarantee justice.
It does not guarantee privacy.
It does not guarantee security.
It does not guarantee equality.
It does not eliminate power.
It prevents certain forms of power from becoming absolute.
Privacy establishes the individual’s boundary.
Cryptography protects that boundary.
Decentralization prevents one authority from controlling the entire architecture.
Open protocols preserve alternatives.
Technological exit constrains the gatekeeper.
Decentralization is a check on power.
Foundational Sources and Influences
- Madison, James. “The Structure of the Government Must Furnish the Proper Checks and Balances Between the Different Departments.” The Federalist No. 51, February 6, 1788.
https://guides.loc.gov/federalist-papers/text-51-60 - Baran, Paul. On Distributed Communications: I. Introduction to Distributed Communications Networks. RAND Corporation, 1964.
https://www.rand.org/pubs/research_memoranda/RM3420.html - Ostrom, Elinor. Governing the Commons: The Evolution of Institutions for Collective Action. Cambridge University Press, 1990.
https://doi.org/10.1017/CBO9780511807763 - Saltzer, Jerome H., David P. Reed, and David D. Clark. “End-to-End Arguments in System Design.” ACM Transactions on Computer Systems, Vol. 2, No. 4, 1984, pp. 277–288. DOI: 10.1145/357401.357402.
https://dl.acm.org/doi/10.1145/357401.357402 - May, Timothy C. The Crypto Anarchist Manifesto. Written in 1988 and circulated electronically to the Cypherpunks mailing list in 1992.
https://cryptochainuni.com/crypto-anarchist-manifesto/ - Hughes, Eric. A Cypherpunk’s Manifesto. March 9, 1993.
https://cryptochainuni.com/cypherpunk-manifesto/ - Barlow, John Perry. A Declaration of the Independence of Cyberspace. February 8, 1996.
https://constitutioncenter.org/the-constitution/historic-document-library/detail/a-declaration-of-the-independence-of-cyberspace-1996 - Lessig, Lawrence. Code and Other Laws of Cyberspace. Basic Books, 1999.
https://cyber.harvard.edu/publications/1999/Code_And_Other_Laws_Of_Cyberspace - Cohen, Bram. “Incentives Build Robustness in BitTorrent.” Workshop on Economics of Peer-to-Peer Systems, 2003.
https://www.cs.princeton.edu/courses/archive/fall17/cos561/papers/BitTorrent03.pdf - Dingledine, Roger, Nick Mathewson, and Paul Syverson. “Tor: The Second-Generation Onion Router.” Proceedings of the 13th USENIX Security Symposium, 2004.
https://www.usenix.org/conference/13th-usenix-security-symposium/tor-second-generation-onion-router - Benkler, Yochai. The Wealth of Networks: How Social Production Transforms Markets and Freedom. Yale University Press, 2006.
https://cyber.harvard.edu/wealth_of_networks/Download_PDFs_of_the_book - Nakamoto, Satoshi. “Bitcoin: A Peer-to-Peer Electronic Cash System.” 2008.
https://bitcoin.org/bitcoin.pdf - Buterin, Vitalik. “A Next-Generation Smart Contract and Decentralized Application Platform.” Ethereum Whitepaper, 2014.
https://ethereum.org/en/whitepaper/ - Benet, Juan. “IPFS—Content Addressed, Versioned, P2P File System.” Draft paper, July 2014.
https://arxiv.org/abs/1407.3561 - Ethereum Foundation. “Ethereum Launches.” July 30, 2015.
https://blog.ethereum.org/2015/07/30/ethereum-launches